Audit log
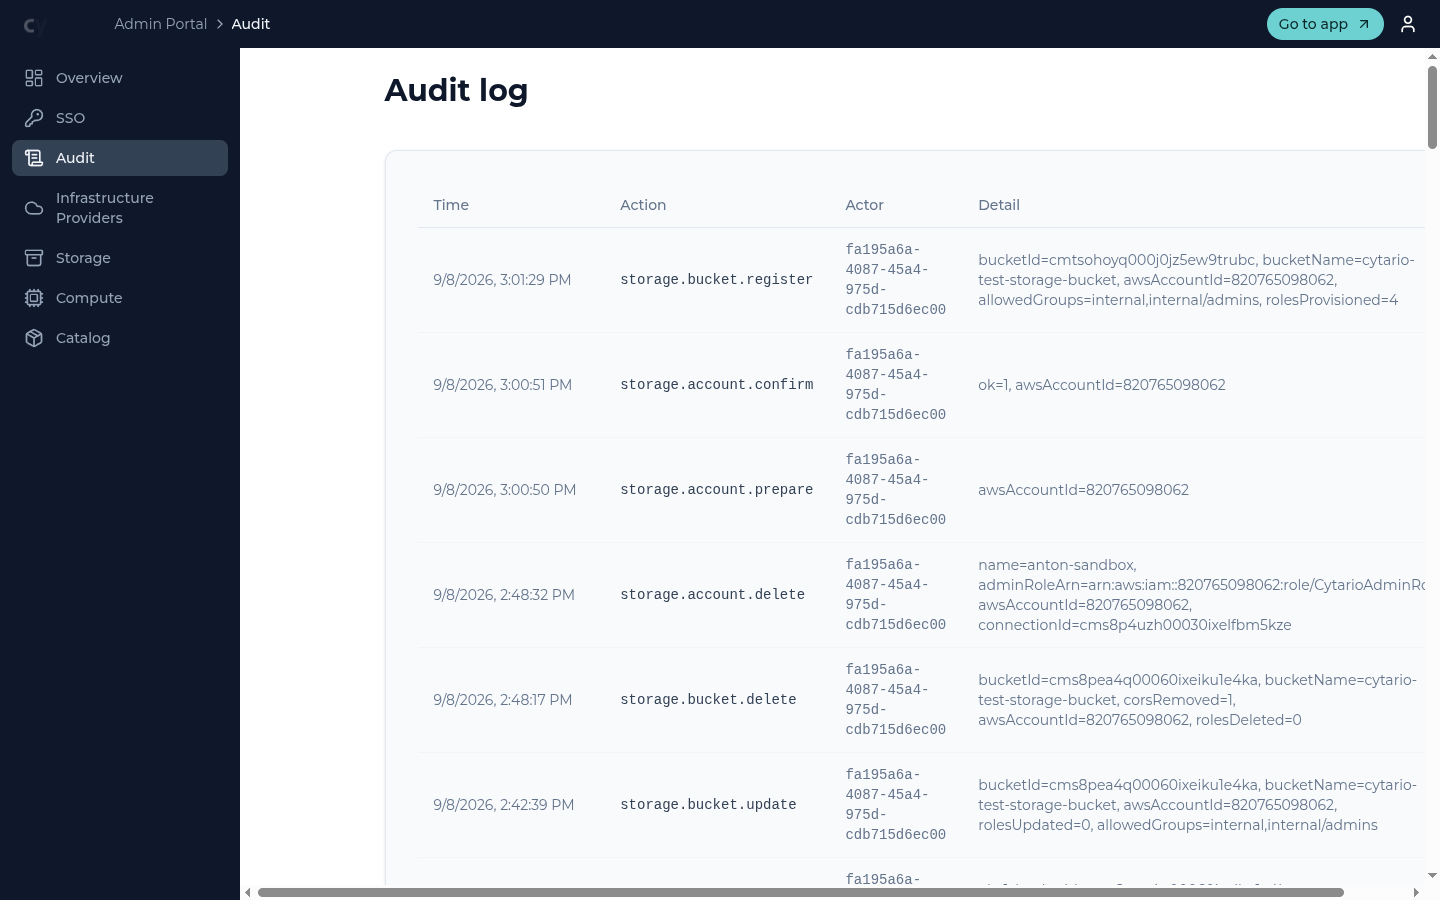
The Audit section records the actions taken in your organization's platform-managed storage and single sign-on, most recent first, to support accountability and review.
What the log records
Each entry captures:
| Column | Meaning |
|---|---|
| Time | When the action happened |
| Action | The action type, for example storage.account.confirm, storage.role.create, storage.bucket.register, or single sign-on lifecycle actions such as sso.config.configure, sso.domain.verify, sso.enable |
| Actor | The account that performed it |
| Detail | The specifics (account, role name/ARN, write level, bucket, and more) |
The log is read-only — it records what happened for review; you do not edit or delete entries from here. Organization and storage lifecycle events appear here automatically, giving an auditable trail of how your organization's storage was configured over time.